Enterprise Employee Relations Software
Graylark is an employee relations and labour relations management platform designed for multinational organisations. It helps HR, Employee Relations, and Legal teams manage employee representative engagement, consultation workflows, and documentation in a single auditable system.
In complex organisations, employee relations work is rarely a single workflow. It spans multiple regions, multiple stakeholders, and multiple legal requirements. Graylark provides a structured way to manage that complexity without relying on email chains, spreadsheets, and disconnected file stores.
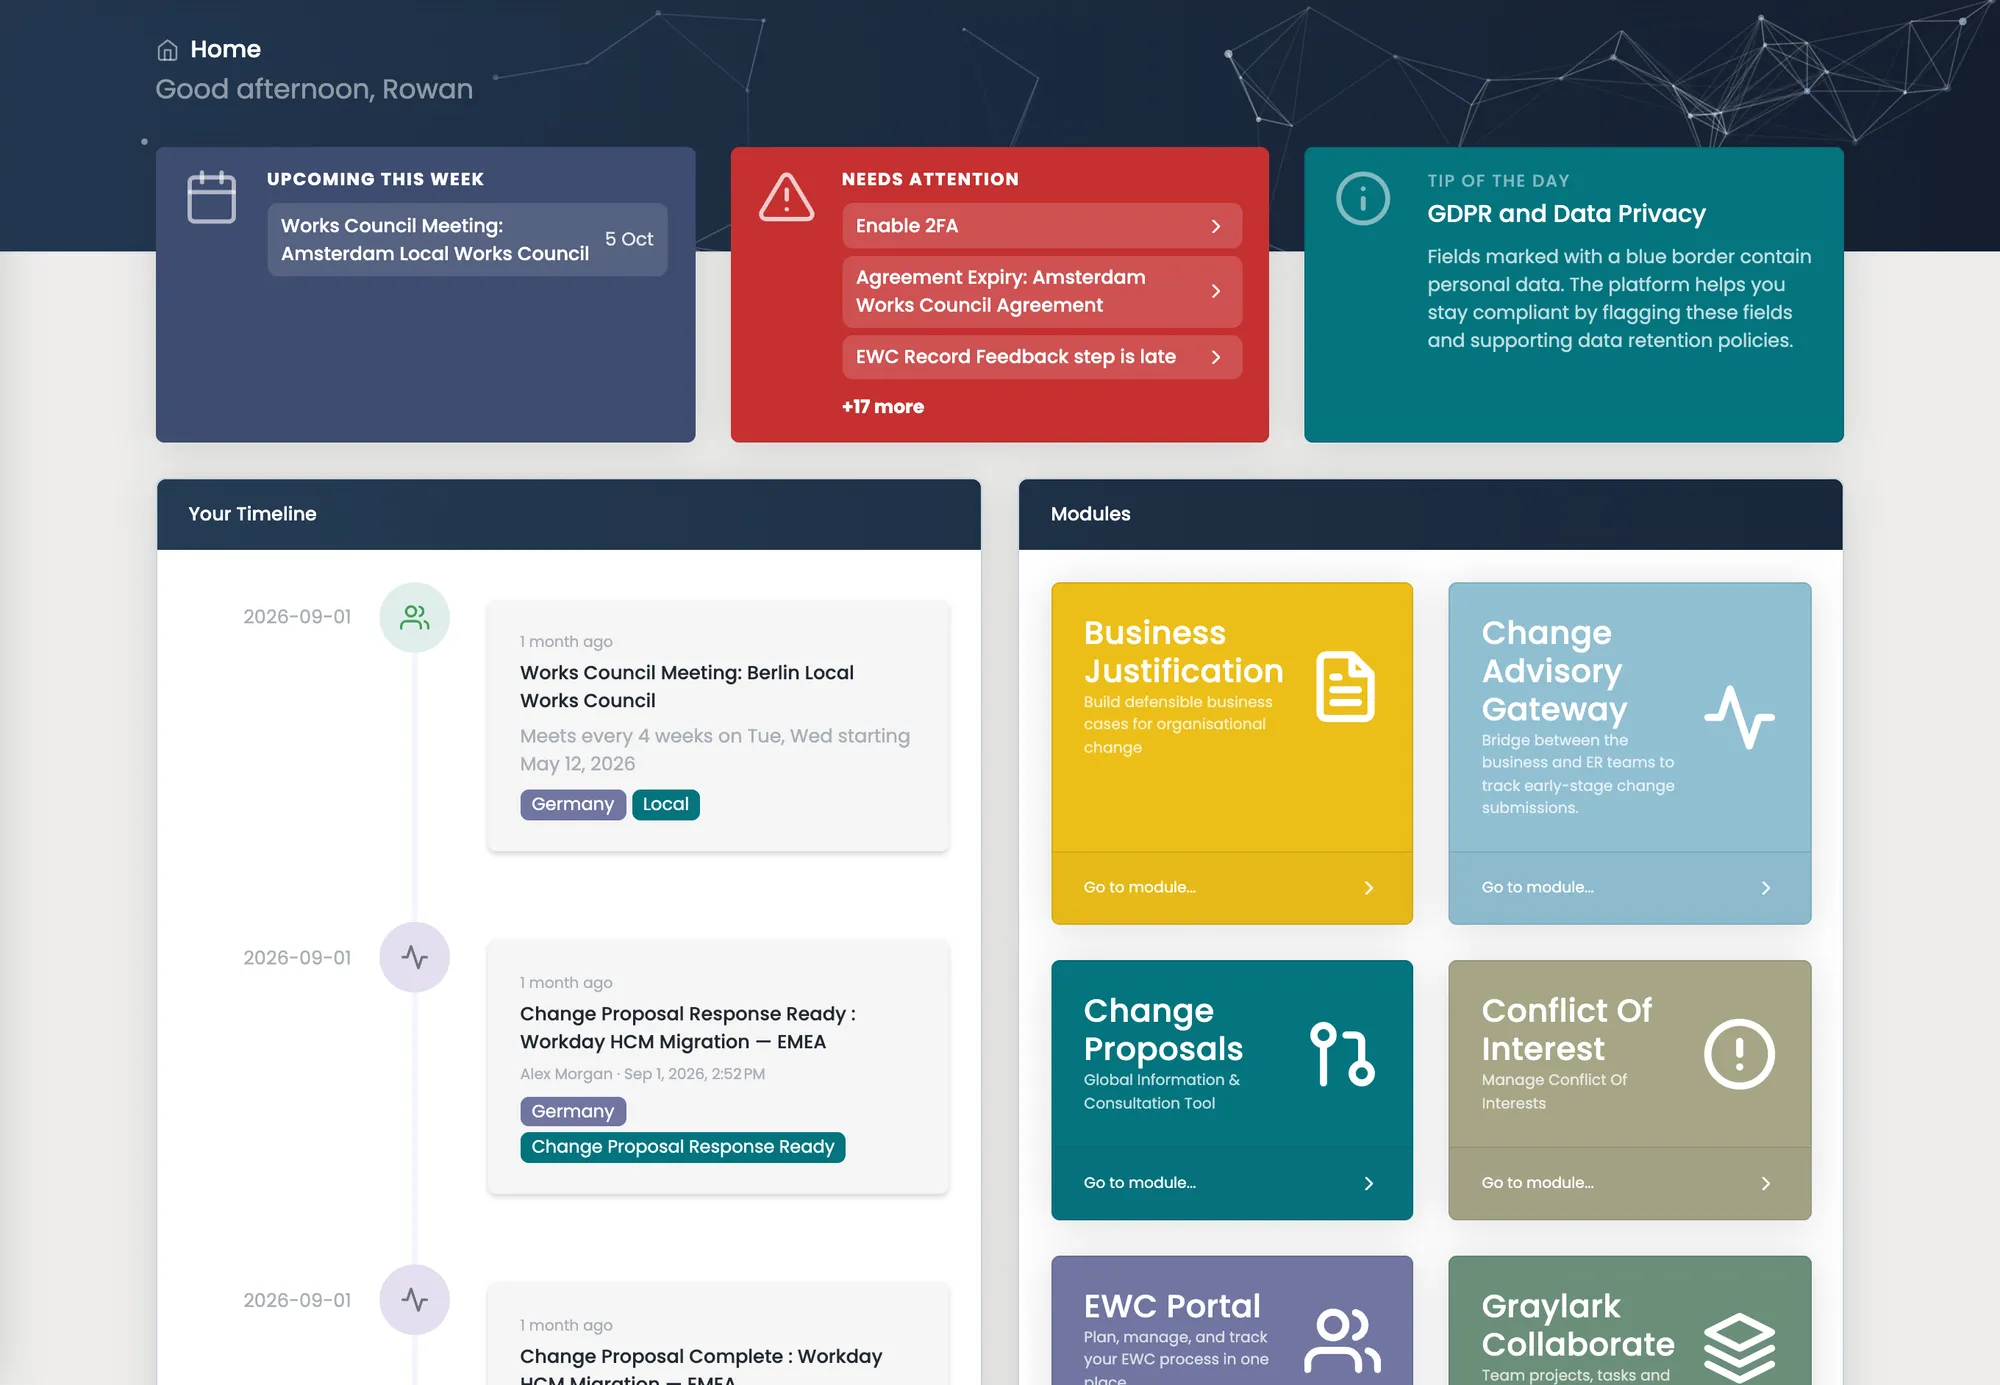
What teams use Graylark for
- Managing employee representative engagement across countries and business units
- Coordinating consultation milestones, deadlines, and dependencies
- Maintaining consistent documentation and decision records
- Supporting workforce change, policy updates, and technology rollouts
- Reducing operational risk with clear ownership and audit trails
Key Capabilities
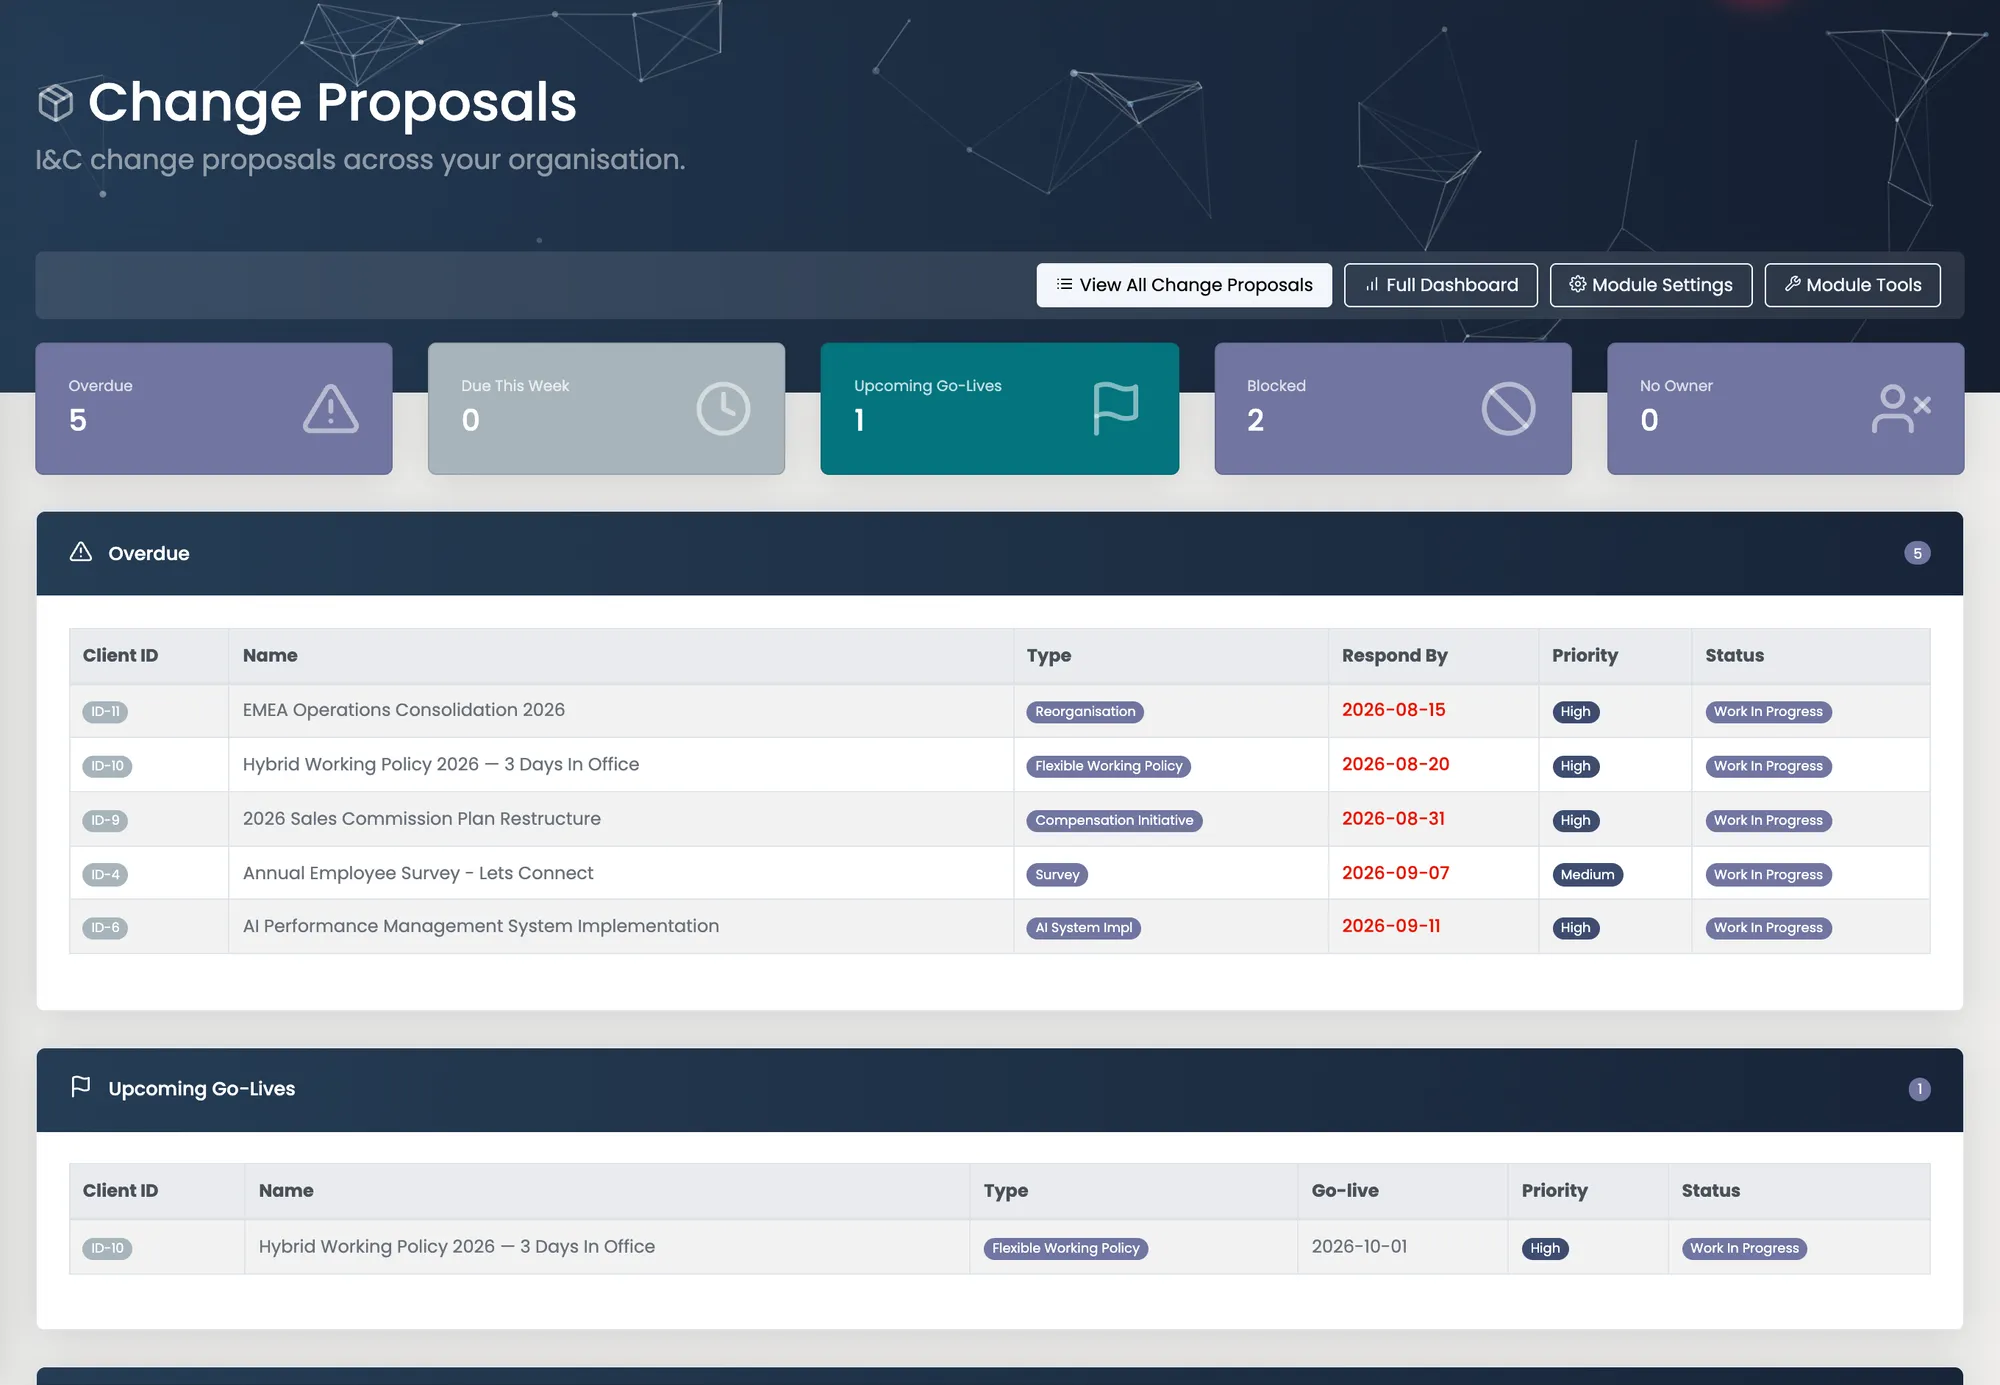
Structured workflows
Create repeatable processes for consultation and engagement so critical steps don’t get missed.
Centralised documentation
Store meeting records, documents, decisions, and outcomes in one place, linked to the relevant activity.
Stakeholder coordination
Bring HR, Legal, Communications, and business leaders into the same process with clear responsibilities.
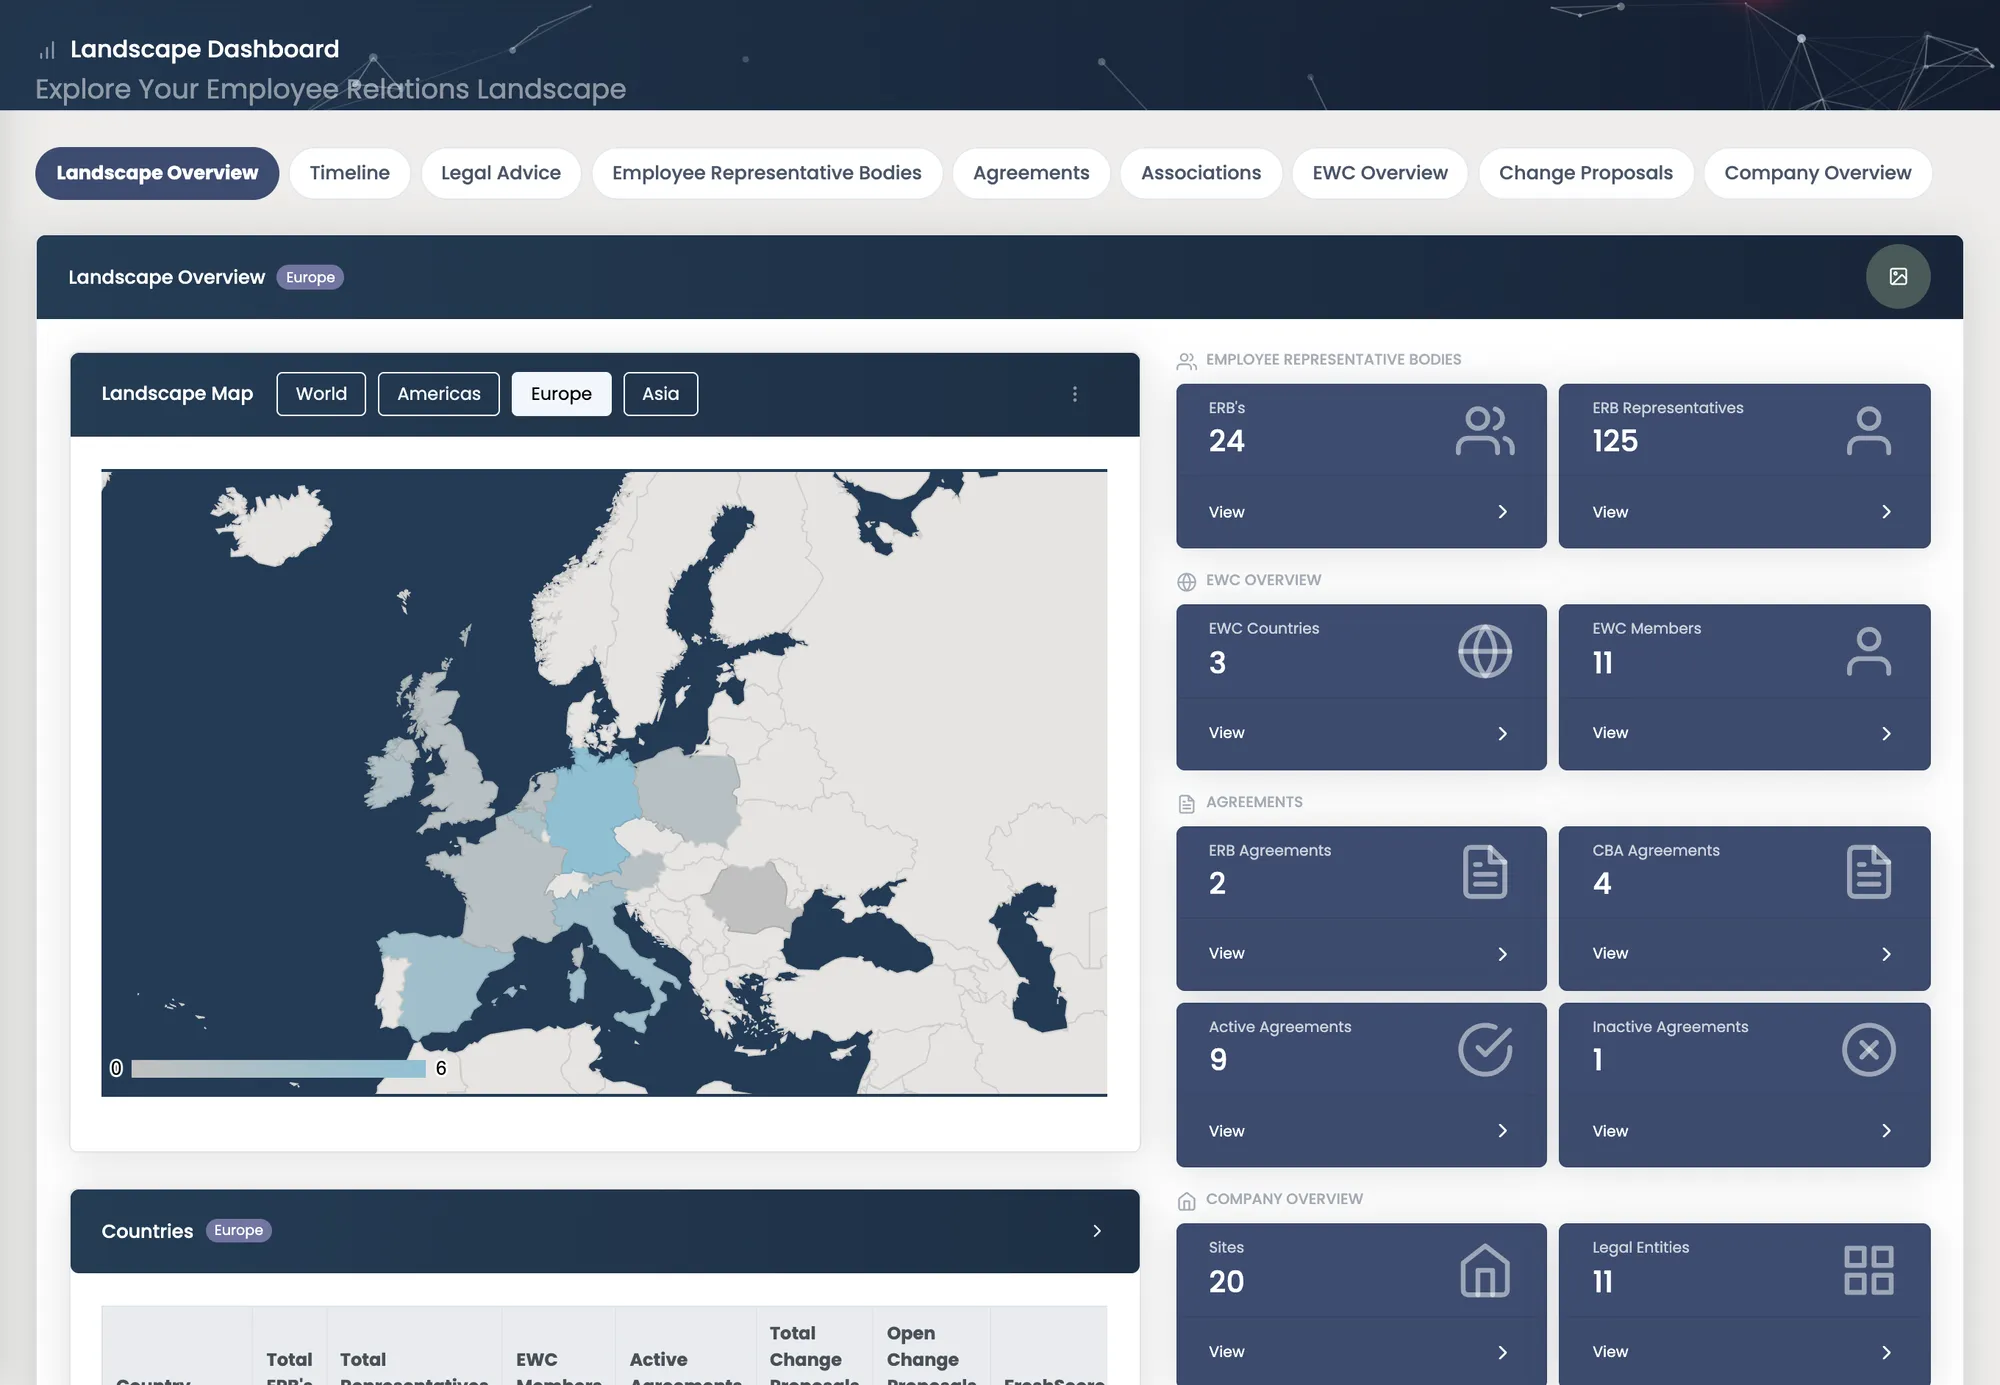
Visibility and reporting
Track status across regions and initiatives so leaders can see where consultation stands and what’s at risk.
Typical users
Employee Relations leaders, HR Business Partners, corporate legal teams, and compliance stakeholders in organisations operating across multiple jurisdictions.
See it in Graylark.
Built for scrutiny.
Certified and tested
Cyber Essentials certified at Whole Organisation scope, and an independent penetration test of the platform in 2026.
Data inside the EEA
Stored and processed within the European Economic Area, with a dedicated database for each customer.
AI that stays inside
Inference inside Graylark’s EEA environment, no external AI APIs in the customer-data path, and no training on customer data.
Ready for procurement
The security pack, the Data Processing Agreement and the penetration test report are standing documents, sent the same day your security team asks.