Workforce Change Consultation Management
Workforce change creates consultation obligations, governance risk, and intense coordination pressure across HR, Legal, Communications, and leadership. Graylark helps teams manage consultation requirements during organisational change with structured workflows, consistent documentation, and an audit-ready record of decisions.
Whether you’re preparing a restructure, rolling out a new policy, or introducing technology that impacts employees, consultation becomes a critical path activity. The cost of missed steps isn’t only delay. It’s risk.
Examples of workforce change scenarios
- Reorganisation and restructuring programmes
- Policy changes (working time, performance, conduct, benefits)
- Technology rollouts that impact employees (including AI-enabled tools)
- Changes to roles, locations, reporting lines, or operating models
- Cross-border programmes requiring coordinated consultation and reporting
How Graylark helps
End-to-end consultation workflows
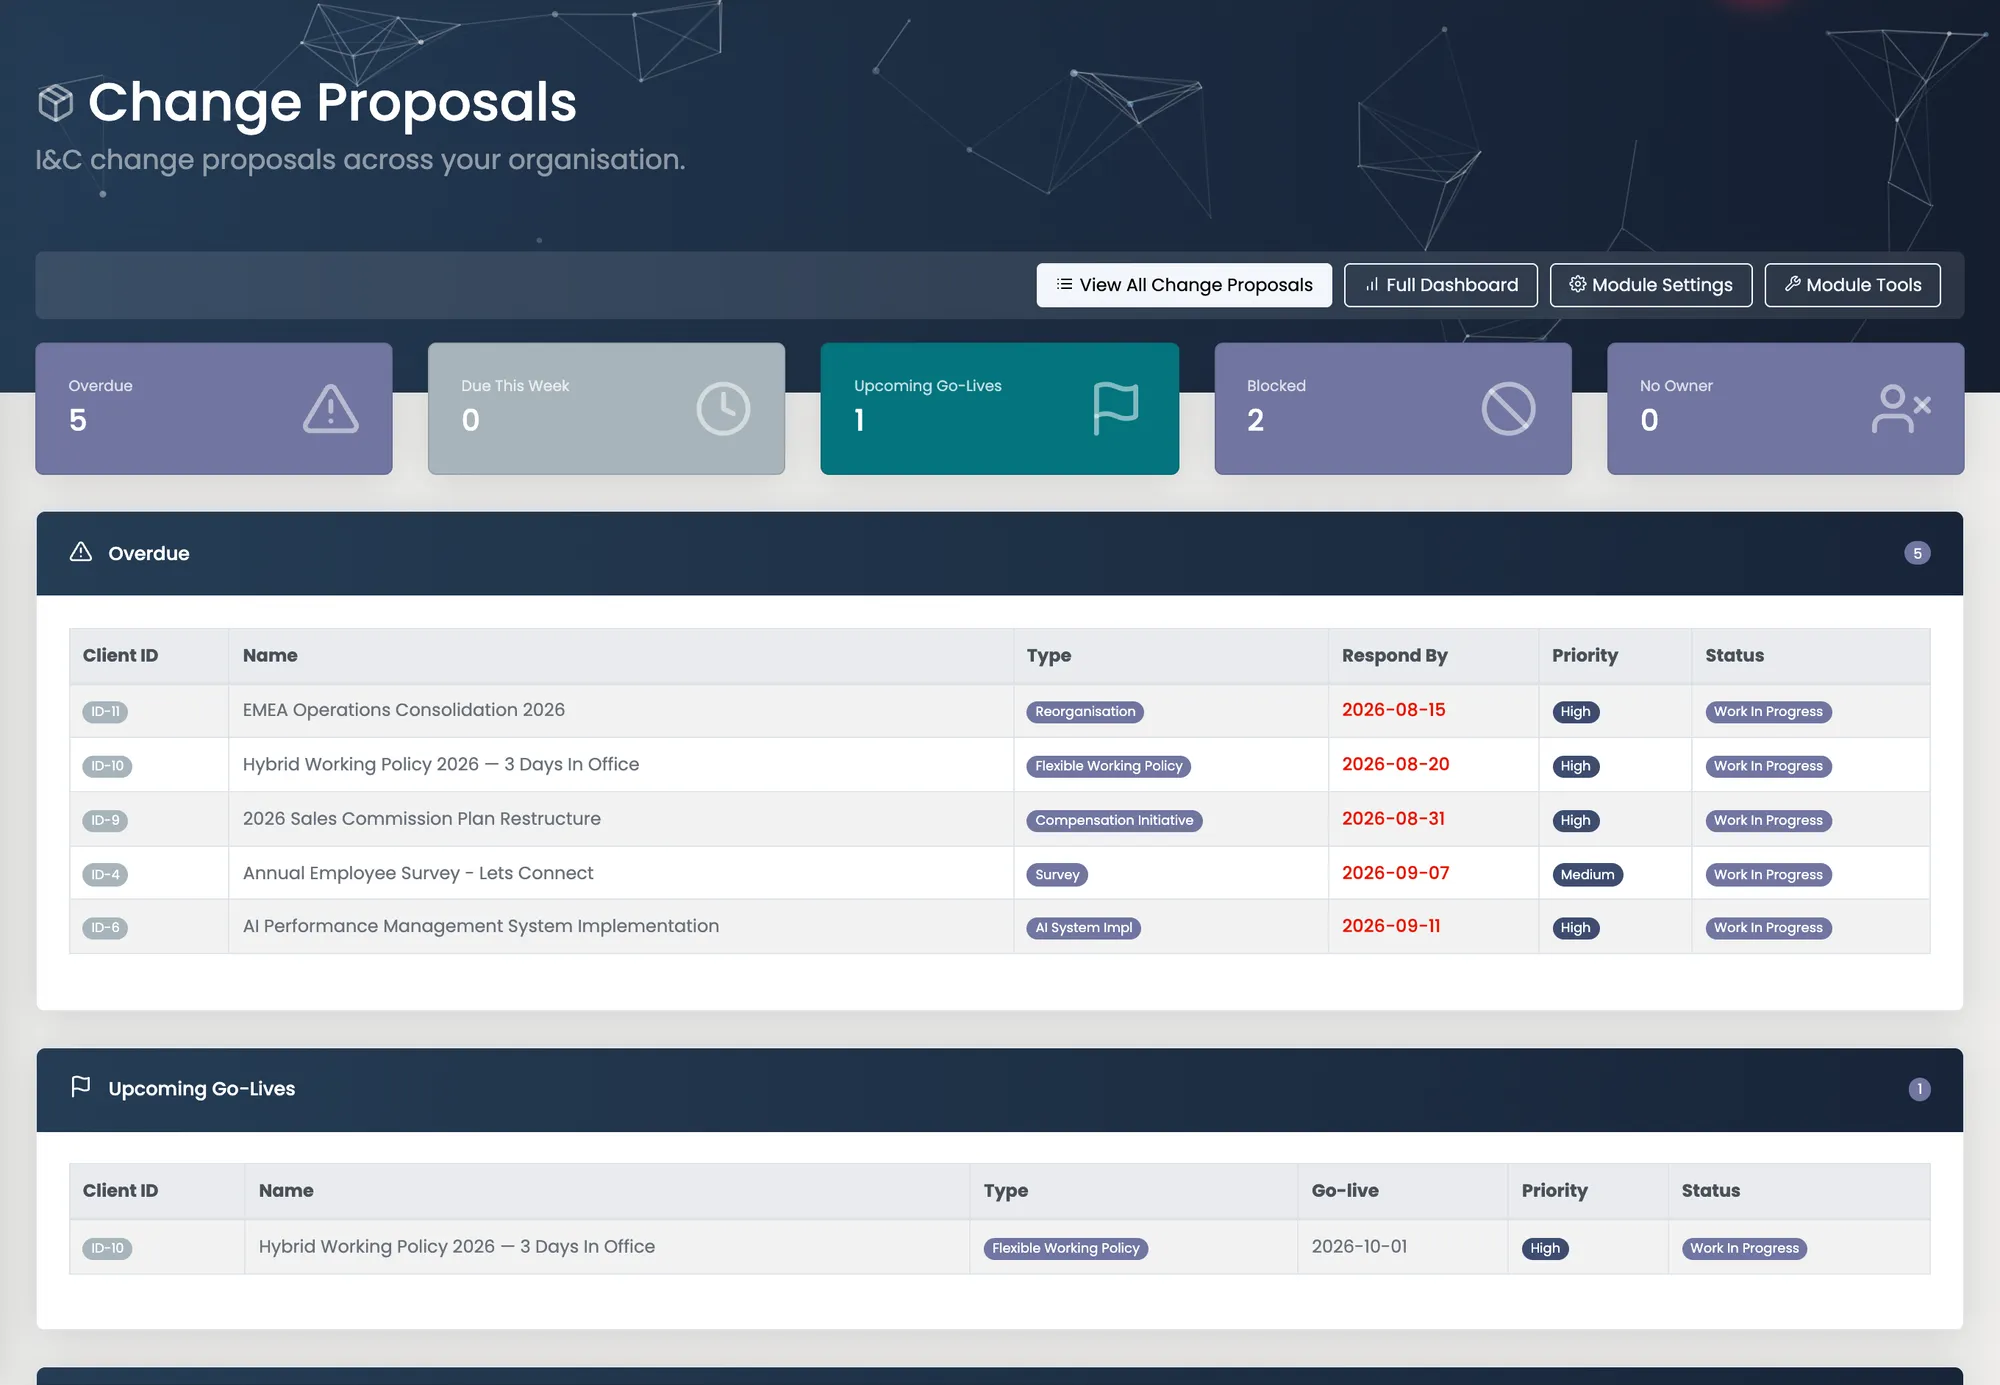
Track required steps, dependencies, owners, and deadlines so consultation is managed like a programme, not an email thread.
Centralised documentation and outcomes
Maintain one place for documents, meeting records, decisions, and agreements connected to the change activity.
Stakeholder coordination
Bring together HR, ER, Legal, and business owners with clear tasks and accountability.
Visibility for leadership
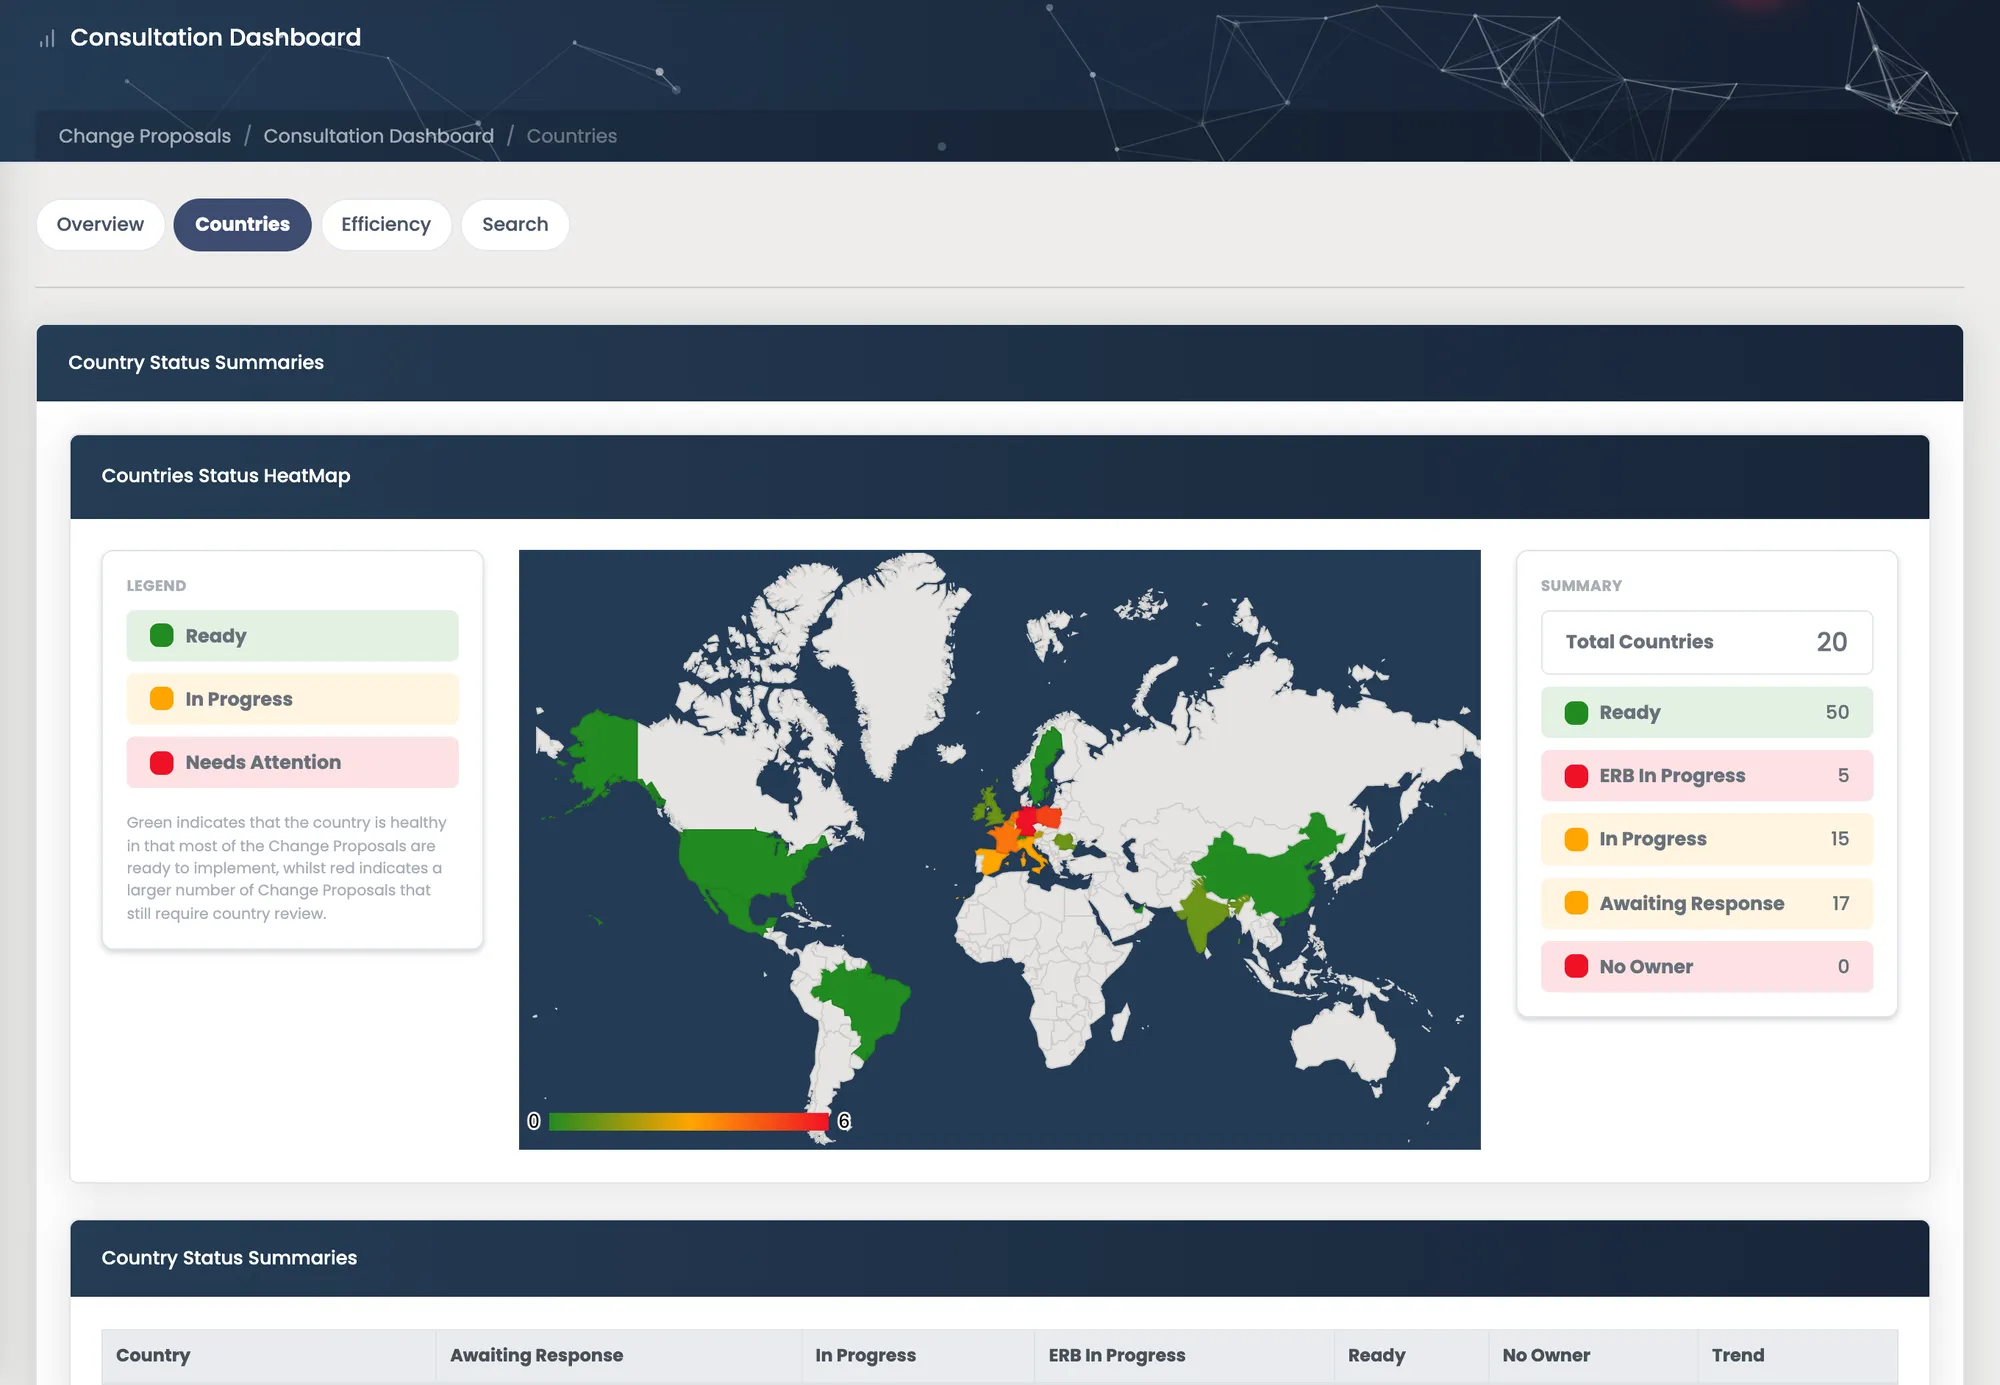
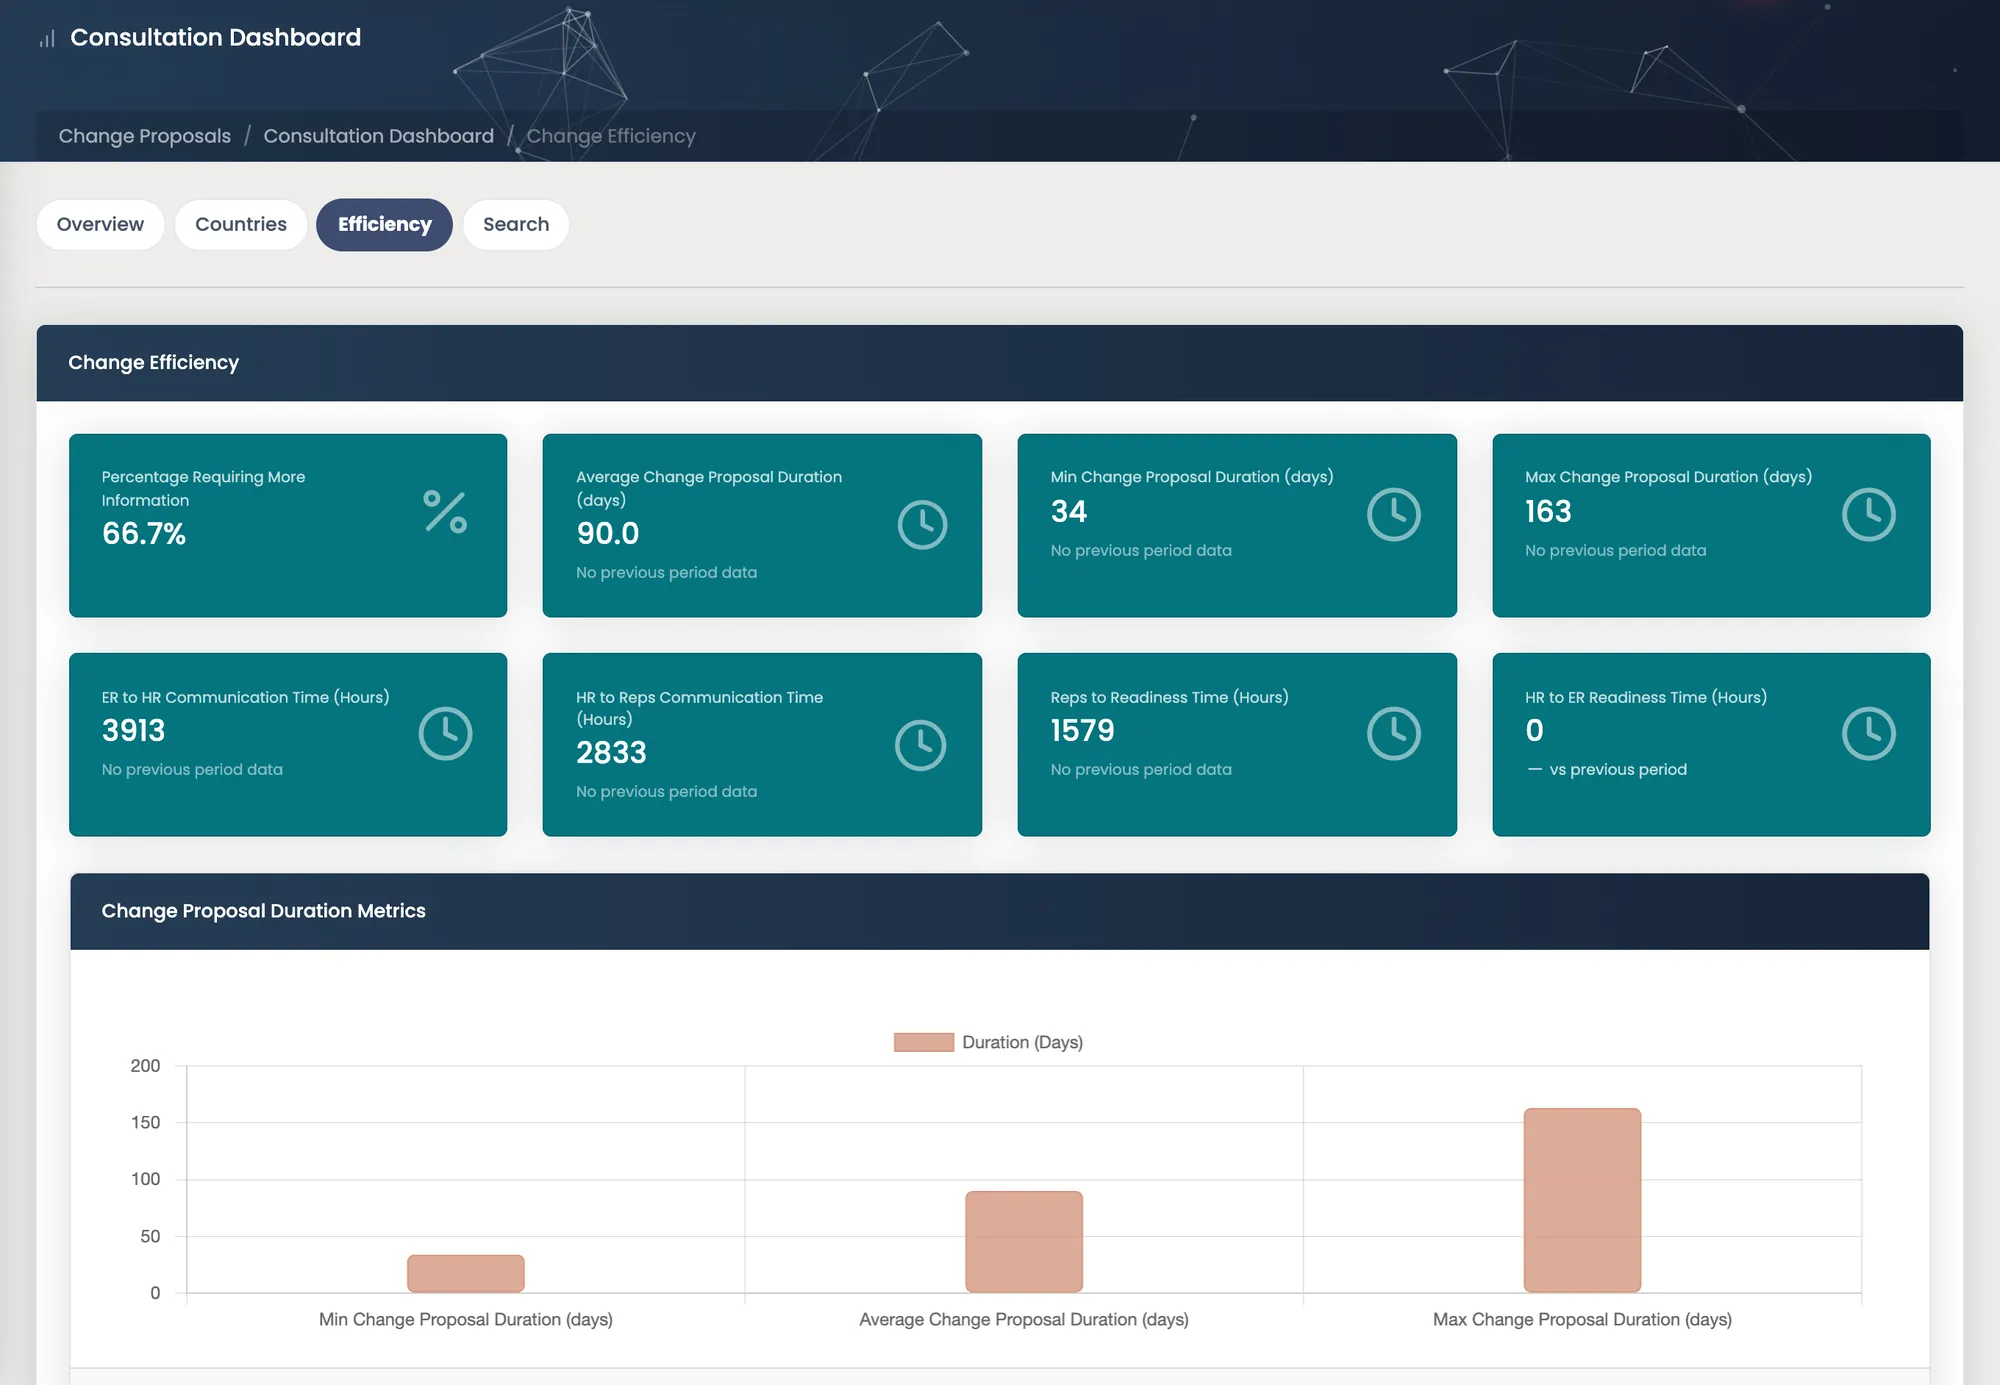
Provide reporting and status tracking across multiple concurrent initiatives, regions, and representative bodies.
See it in Graylark.
Built for scrutiny.
Certified and tested
Cyber Essentials certified at Whole Organisation scope, and an independent penetration test of the platform in 2026.
Data inside the EEA
Stored and processed within the European Economic Area, with a dedicated database for each customer.
AI that stays inside
Inference inside Graylark’s EEA environment, no external AI APIs in the customer-data path, and no training on customer data.
Ready for procurement
The security pack, the Data Processing Agreement and the penetration test report are standing documents, sent the same day your security team asks.